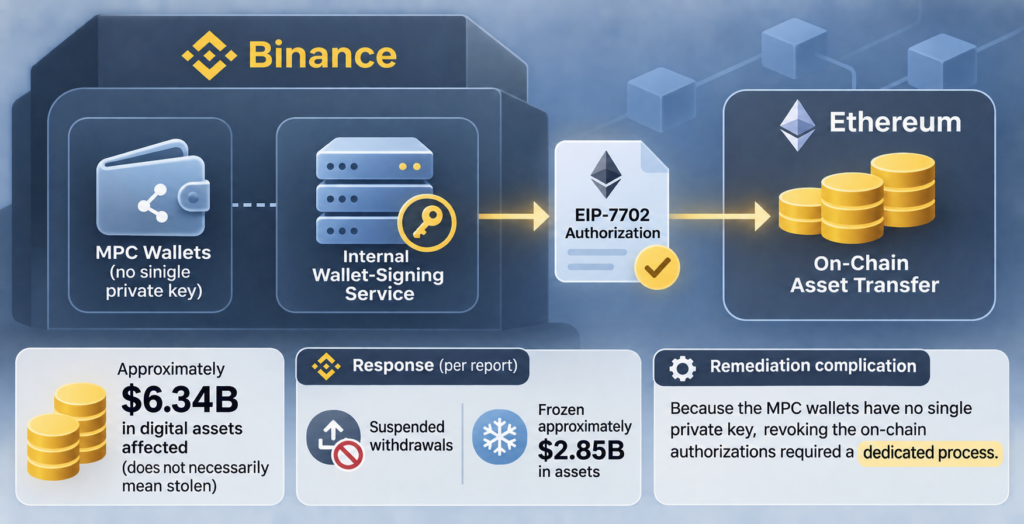
For builders, the key technical issue in a Binance security report is how access to an internal wallet-signing service and Ethereum’s EIP-7702 authorization mechanism figured in asset transfers. The report, published on November 5, 2026, describes an October 29 incident affecting approximately $6.34 billion in digital assets. “Affected” does not necessarily mean stolen.
According to the report, the attackers gained access to the wallet team in stages through a fake job interview, a malicious code repository, a compromised internal AI tool and endpoint intrusion. They then used the internal signing service and EIP-7702 authorizations to transfer assets.
Binance suspended withdrawals and froze approximately $2.85 billion in assets, the report says. It also notes a complication for remediation: because its multi-party computation (MPC) wallets have no single private key, revoking the on-chain authorizations required a dedicated process. The report discusses attack preparations, an alleged North Korea connection, response measures and a subsequent independent security review, but the supplied account does not provide further details of those findings.