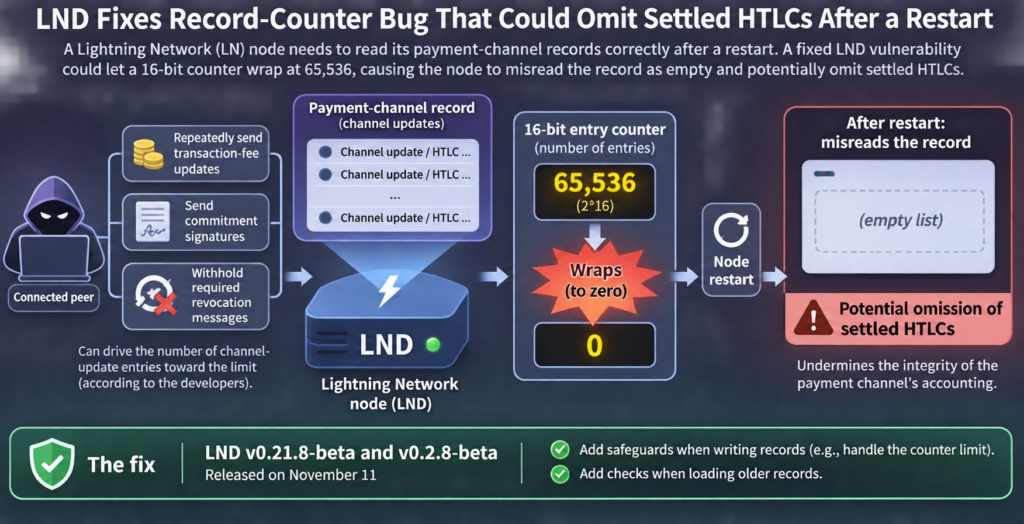
A Lightning Network node needs to read its payment-channel records correctly after a restart. In a report published on November 17, 2026, ChainCatcher, citing CryptoSlate, said developers had fixed an LND vulnerability that could cause a node to misread those records.
The issue involved a 16-bit counter used to record the number of entries when channel updates were saved and restored. At 65,536 entries, the counter could wrap to zero. After a restart, the node could then interpret the record as an empty list and omit settled hashed timelock contracts (HTLCs)—conditional payments tracked by the channel—undermining the integrity of its channel accounting.
According to the developers, a connected peer could drive the entry count toward that limit by repeatedly sending transaction-fee updates and commitment signatures while withholding required revocation messages. LND released v0.21.8-beta and v0.2.8-beta on November 11 with safeguards when writing records and checks when loading older records. At the time of the November 17 report, it had not been confirmed whether the vulnerability had been exploited or caused any loss of funds.